> For the complete documentation index, see [llms.txt](https://docs.parallels.com/landing/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.parallels.com/landing/pd-ag/getting-started/configuring-the-single-sign-on-sso-integration-with-parallels-my-account/starting-the-integration-process-in-parallels-my-account/configuring-sso-integration-with-azure-entra-id.md).
# Configuring SSO Integration with Azure/Entra ID
Follow the steps below one by one to integrate Parallels My Account with Microsoft Entra ID.
### (1) Configure Organization's Domain(s)
A domain is a part of the email addresses (after the @ symbol) used by the end users in your organization. When end users try to log in to Parallels My Account using SSO, they are prompted to enter their work email address. Parallels My Account checks the domain part of the email address and recognizes that the user belongs to your organization. Click on the title of **Step 1** to expand it and read the instructions carefully.
* Add one or more domains your organization uses.
* Each domain must be unique and can only be registered to **one** business account that your organization has registered with Parallels.
* Make sure to add only the domains your organization can control.
The Parallels My Account service verifies the domain ownership by checking a specific TXT record that must be added to the DNS host of the corresponding domain. Make sure that all domains added to the list are verified before proceeding with the next steps.
Depending on the software and/or provider, a TXT record may take up to 72 hours to propagate. You can check whether it's been configured using the following command:
```
$ dig TXT {yourdomain}.{com}
```
### (2) Register Parallels Enterprise App
Registering the Parallels enterprise application (required for integrating with the Parallels My Account service) in the IdP Directory allows you to configure the SSO-related parameters and correctly provision the integration between your IdP and the Parallels My Account service. The description below illustrates the registration procedure for Microsoft Entra ID. It is assumed that you have the permissions required to register and configure enterprise applications with Entra ID. To register a Parallels enterprise application with Microsoft Entra ID:
1. Log into the Microsoft Entra ID portal using an account that has the privileges required to register and configure enterprise applications for your organization.
2. On the [Home page](https://portal.azure.com/#home), choose Microsoft Entra ID from the services gallery to open the landing page.
3. Choose **Enterprise applications** in the **Manage** section on the left-hand side panel to open the page with the list of the enterprise applications registered with your organization.
4. Click **New application** above the list of registered applications to open the **Browse Entra ID Gallery** page which allows you to add a new app.
5. Click **Create your own application** to start the procedure of registering a new custom enterprise app. The popup panel **Create your own application** opens on the right.
6. Type the name of the application (the actual name remains at your discretion), choose the Integrate any other application you don't find in the gallery (**Non-gallery**) option, click **Create** and wait while the new enterprise application is being created. You will end up on the landing page of your new Parallels enterprise application.
Once the Parallels enterprise application registration in the IdP Directory is completed, switch back to the integration [configurator page](https://my.parallels.com/profile/business/idp_integration) at Parallels My Account, expand the section of **Step 2**, and select the **Configuration in the IdP Directory is done** option at the bottom of the section. Then proceed to the next step.
### (3) Configure User Groups Mapping
You must create user groups associated with the Parallels Desktop application in your IdP Directory. Later, you will add users to those groups to let Parallels My Account know which users should have business account admin privileges in the Parallels ecosystem. At least one user group is required for adding users with admin access to your organization’s business account registered with Parallels. Once the group is created, you should add the group's name and ID in **Step 3** of the integration configurator page in Parallels My Account.
Start with creating the group in the IdP Directory. To do so, switch to your IdP management portal and follow the standard procedure of creating a user group and associating it with the Parallels enterprise application, as provided by your Organization’s IdP. The description below illustrates the registration procedure for Microsoft Entra ID. It is assumed that you have appropriate permissions that allow you to manage user groups in Entra ID. To create a user group for the Parallels enterprise application in Microsoft Entra ID:
1. Log into the Microsoft Entra ID portal using the account which has privileges for managing user groups and configuring enterprise applications. 9
2. On the [Home page](https://portal.azure.com/#home), choose **Microsoft Entra ID** in the services gallery to open the Entra ID landing page.
3. Choose **Groups in the Manage** section on the left-hand side panel to open the page with the list of the user groups registered in your tenant.
4. Click **New group** above the list of registered groups to open the page for creating a new group.
5. When on the page for creating a new group, specify:
1. Group type: `Security`,
2. Name and description of the group at your discretion,
3. Membership type: `Assigned`.
6. Click **Create** and wait while the group is being created.
7. Once the group is created, it appears on the list of groups automatically. Select the group from the list (click on it) to open the page with the group’s properties.
8. Repeat steps 3, 4, 5, and 6 once again. Your goal is to set up two groups, one for the **admins** of your organization’s Parallels business account and another for the **users** of Parallels Desktop for Mac Enterprise Edition, who will be granted permission to activate their copies via SSO. If your admins also need to be able to use Parallels Desktop for Mac, add them to both groups.\
\
**Note**: Please make sure that the respective group names on the IdP side and the Parallels My Account side match precisely. This will help you avoid potential problems, as some IdPs use group names in their identification and authorization processes.
9. Copy the names of the specified groups and the **Object ID** (assigned automatically) to Parallels My Account. To do so, switch back to the Parallels My Account integration [configuration page](https://my.parallels.com/profile/business/idp_integration), expand the **Step 3** section, click on **Click to edit** on the respective group, paste the group name and ID into the corresponding input fields, and click **Save**.\
\
Repeat twice for the **Parallels Business Account Admins** and **Parallels Desktop Users** groups.
10. Switch back to the Microsoft Azure portal and associate both groups with the Parallels app. To do so:
1. Choose **MS Azure Home** > **Entra ID** > **Enterprise applications**;
2. Select the Parallels application from the list and click on it to open its home page;
3. Select **Users and groups** on the side panel on the left;
4. Click **Add user/group**;
5. In **Add Assignment**, click on **None Selected** under **Users and Groups** to launch group selection;
6. Select the groups created in **Step 4**, and click **Select**;
7. Finally, click **Assign**.
\
Make sure to link both groups, the administrators and the users.
11. While on the Parallels application’s home page in MS Azure Home, select **Properties** in the left-hand side panel, scroll down to the **Assignment Required** setting, and make sure it’s enabled.
12. On the same page, make sure that the **Visible to users** option is disabled.
13. Click **Save** at the top of the page.
Once the required groups have been created in the IdP Directory and associated with the Parallels app, switch back to the Parallels My Account [integration configurator page](https://my.parallels.com/profile/business/idp_integration). If everything is set, move on to the next step.
### (4) Configure SAML Integration
SAML 2.0 integration between Parallels My Account and your organization’s IdP allows your organization's users to activate their copies of Parallels Desktop for Mac Enterprise Edition using Single Sign-On (SSO) while your admins can use it to log into the business account registered with Parallels using their main corporate login credentials.
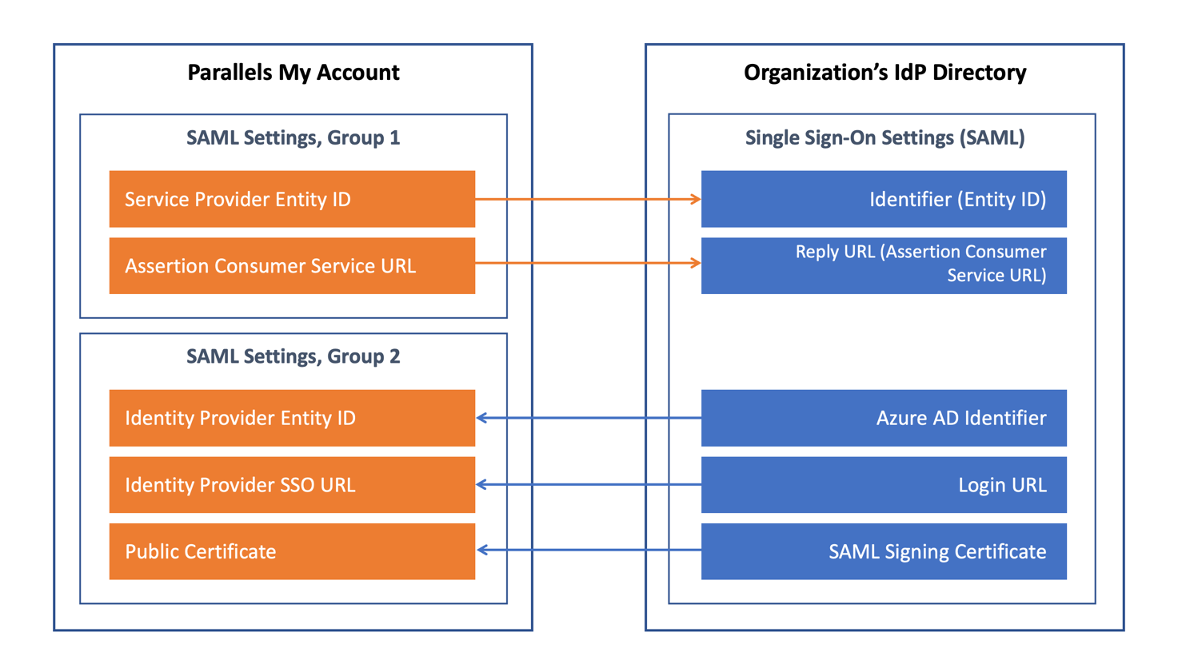
To complete this step, you must copy certain parameters from your Parallels My Account to the settings section of the Parallels application registered in the IdP Directory and then copy certain data provided in the IdP Directory to the Parallels My Account admin panel.
The following description illustrates the procedure for Entra ID. It is assumed that you have appropriate permissions that allow you to configure enterprise applications in Entra ID. If your organization uses a different IdP service, follow the instructions provided in the admin guide specific to your IdP of choice.
Expand the **Step 4** section on the [integration configurator page](https://my.parallels.com/profile/business/idp_integration) in Parallels My Account. Note that there are two groups of parameters in the section. The first group has two values, **Service Provider Entity ID** and **Assertion Consumer Service URL**, which must be copied from Parallels My Account to the IdP Directory. The second group includes three parameters – **Identity Provider Entity ID**, **Identity Provider SSO URL**, and **Public Certificate**. The values for these parameters must be copied from your IdP Directory to Parallels My Account.
There are two ways to copy the parameters between Parallels My Account and the IdP Directory: via metadata files (assuming your IdP software supports transferring those parameters via external files) or manually.
Begin with copying the first group of parameters — **Service Provider Entity ID** and **Assertion Consumer Service URL** (both values are pre-set automatically and cannot be changed) from Parallels My Account to the IdP Directory.
#### \[RECOMMENDED] Option 1: Copying the data to and from Parallels My Account to Entra ID via a metadata file
Click **Download a metadata file** link in the subtitle of the group to save these parameters to the external metadata file. To transfer the values of the parameters from the metadata file to the IdP Directory, follow these steps:
1. Log into the Microsoft Azure portal using the account which has privileges for configuring enterprise applications.
2. Choose **MS Azure Home** > **Entra ID** > **Enterprise applications**, select the Parallels enterprise application from the list, click on it to open the application’s home page, and choose **Single sign-on** in the **Manage** section on the left-hand side panel to open the page for configuring the Single Sign-On method for the enterprise application.
3. When on the **Single Sign-On** configuration page, choose **SAML** as the Single Sign-On method. The page for configuring a Single Sign-on with SAML will open.
4. Switch to your IdP integration page in My Account, scroll down to, and expand **Step 4** ("`Configure SAML integration`"). Under **Service Provider Settings**, click the **Download a metadata file** link to download the `metadata.xml` file.
5. Return to the **Set up Single Sign-on with SAML** page and click **Upload metadata file** at the top of the page to open the popup dialog that allows you to select the file. Select the file you have previously downloaded from Parallels My Account, then click **Add** to load the data from the selected file. The popup panel opens with the properties of the basic SAML configuration loaded from the metadata file.
6. Check that the following parameters are set: **Identifier** (**Entity ID**), **Reply URL** (**Assertion Consumer Service URL**), and the values of the parameters match those in the respective Parallels My Account section. Click **Save**.
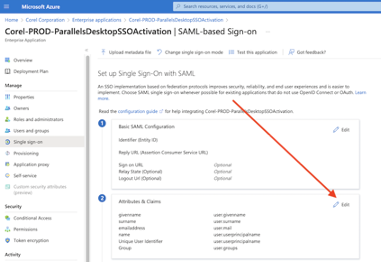
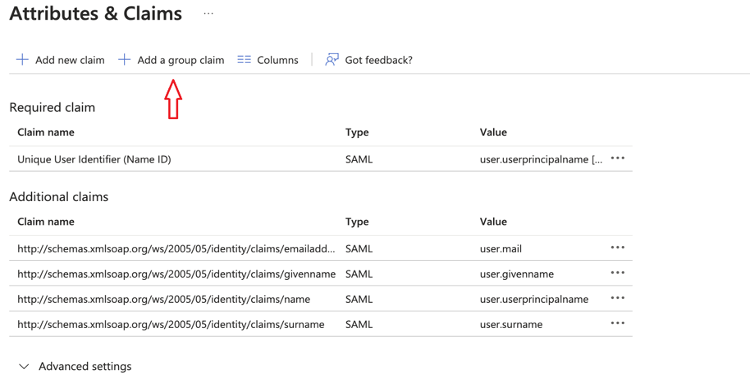
7. On the left pane, choose **Single sign-on**. Select **Attributes and Claims**, then **Edit**, then click **Add a group claim**.
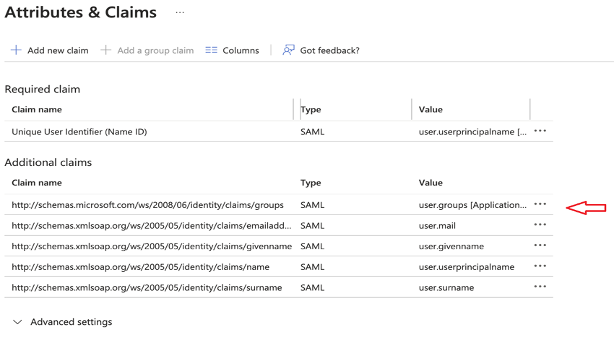
8. In **Group Claims**, select **Groups assigned to application** and click **Save**.\
9. To close the configuration, click **Close** at the top of the panel on the right. Then, return to the **SAML-Based Sign-On** page.
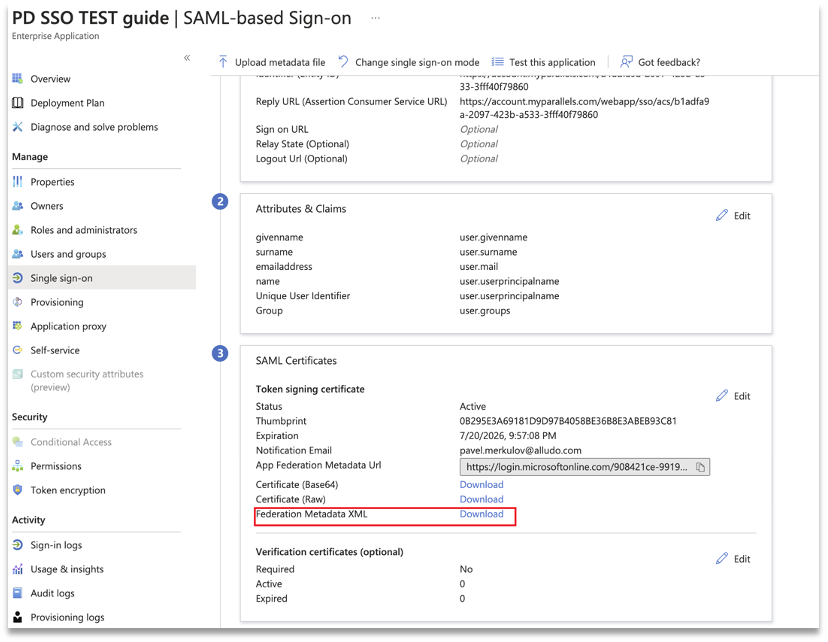
10. On the **SAML-Based Sign-On** page, under the **SAML Certificates** section, locate **Federation Metadata XML** and click **Download**.
11. Switch to your IdP integration page in My Account, scroll down to and expand **Step 4** ("`Configure SAML integration`"). Under **Identity Provider Settings**, click on the **Upload a metadata file** link and select the downloaded XML file.
12. Select the **Configuration in the IdP Directory is done** option at the bottom of the section and click **Save** to finish the configuration. Proceed to the next step.
#### Option 2: Copying data to and from Parallels My Account to Entra ID manually
Alternatively, you can set up the basic SAML configuration manually. To do so, perform steps 1-3 as described above in the [**Option 1** ](#recommended-option-1-copying-the-data-to-and-from-parallels-my-account-to-entra-id-via-a-metadata-fi)section. When on the **Set up Single Sign-on with SAML** page, click **Edit** in the section **(1) Basic SAML Configuration**. A popup panel will open with the properties of the basic SAML configuration (the values won’t be set). Copy the value of the **Service Provider Entity ID** from Parallels My Account to the **Identifier** (**Entity ID**) box in the IdP Directory. Copy the value of **Assertion Consumer Service URL** from Parallels My Account to the **Reply URL** (**Assertion Consumer Service URL**) box in the IdP Directory. Click **Save** at the top of the panel to save the configuration. Close the **Basic SAML Configuration** panel.
Proceed to configure **Attributes & Claims** by adding the “`user.groups`” claim on the xn page in Entra ID as described above (refer to **step 6** above in the [**Option 1**](#recommended-option-1-copying-the-data-to-and-from-parallels-my-account-to-entra-id-via-a-metadata-fi) section).
Next, copy the three parameters from MS Azure’s **Set up Single Sign-on with SAML** settings to My Account. On the **Single Sign-on** page, scroll to **4. Set up Application Name** and copy the value of the **Login URL** to the **Identity Provider SSO URL** field in My Account. Next, copy the value of Entra ID **Identifier** to the **Identity Provider Entity ID** field in My Account. And finally, under the **SAML Certificates** section, click to download the **Certificate (Base64)** file and copy the file’s contents to the **Public Certificate** field in My Account.
Finally, select the **Configuration in the IdP Directory is done** option at the bottom of the section and click **Save** in Parallels My Account to confirm that you have finished the configuration procedure in the IdP Directory. Proceed to the next step.
### (5) Configure SCIM Integration
SCIM 2.0 integration between Parallels My Account and your Organization’s IdP allows you to keep user identity information in Parallels My Account in constant sync with the updates made to user identities in the IdP Directory.
It is assumed that your IdP software supports SCIM. For this reason, the SCIM Support option in the **Step 5** section on the integration configurator page in the Parallels My Account is enabled by default. If your IdP does not support SCIM, disable the option and move on to the next step.
The following description is based on the assumption that SCIM is supported.
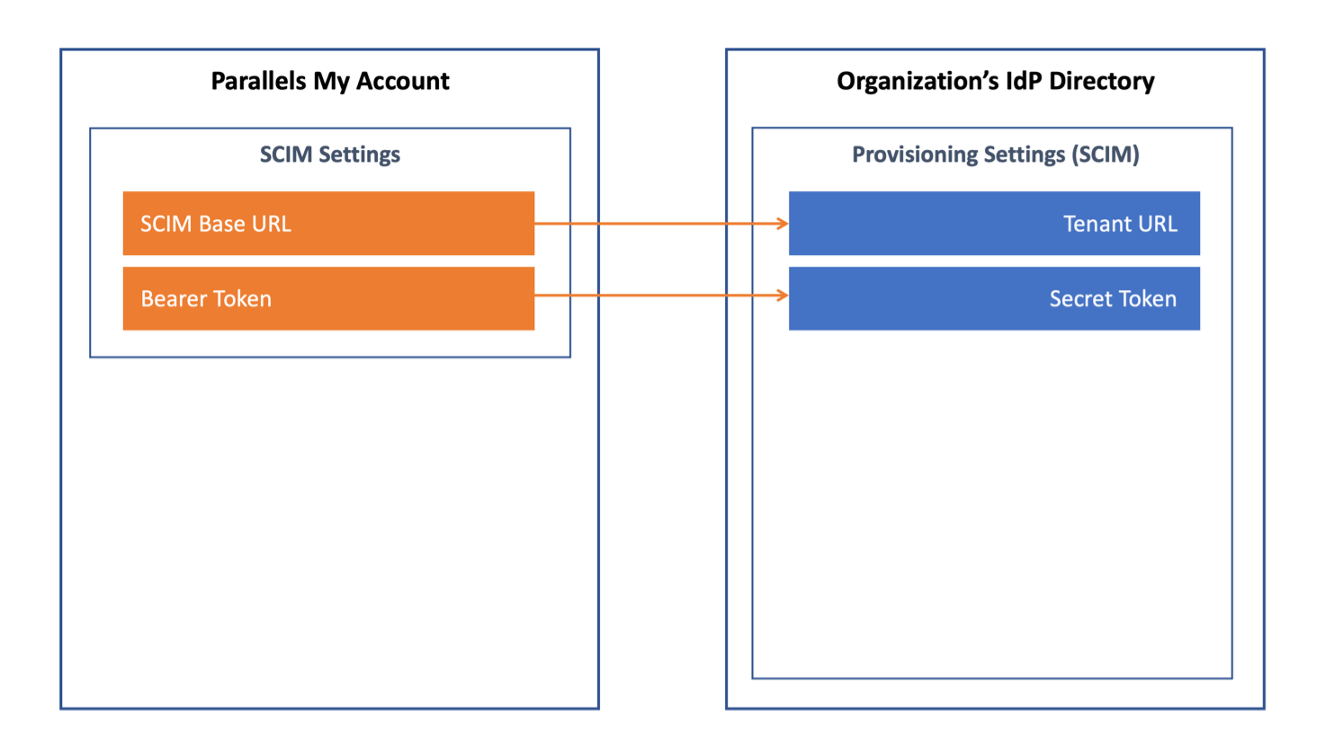
To configure provisioning via SCIM, you must copy two parameters: **SCIM Base URL** and **Bearer Token** (both values are pre-set automatically and cannot be changed) from the **Step 5** section of the [integration configurator page](https://my.myparallels.com/profile/business/idp_integration) in Parallels My Account to the IdP Directory.
The description below illustrates the procedure for Microsoft Entra ID. It is assumed that you have appropriate permissions that allow you to configure enterprise applications in Entra ID. If your organization uses a different IdP service, follow the instructions provided in the admin guide specific to your IdP of choice. To configure SCIM settings at the IdP management portal:
1. Log into the Microsoft Azure portal using the account that has privileges for configuring enterprise applications.
2. Choose **MS Azure Home** > **Entra ID** > **Enterprise applications**. Select the Parallels enterprise application in the list, click on it to open the application’s home page, and choose **Provisioning** in the **Manage** section on the left-hand side panel to open the page for configuring the provisioning settings of the enterprise application.
3. On the **Provisioning** page, click **Get Started**. It opens the page where you can configure the provisioning settings.
4. When on the configuration page, set **Provisioning Mode** to "`Automatic`", then expand the **Admin Credentials** section and set the **Tenant URL** to `SCIM Base URL` (retrieve the value from Parallels My Account), **Secret Token** to `Bearer Token` (retrieve the value from Parallels My Account).
5. Click **Save** to save the changes.
6. \[IMPORTANT] While in the **Manage** section of the **Provisioning** page, open the **Attribute mapping** tab and click on **Provision Microsoft Entra ID Users**. There, under the **Attribute Mappings** section, locate the **externalId** parameter, click **Edit**, change the **Source attribute** parameter from **mailNickname** to **objectId**, and click **OK**. Click **Save** in the top left corner.\
\
Note that without this step, there may be a mixup in product license provisioning between users with similar names.
7. Return to **Overview (Preview)** in the left side panel and click **Start provisioning** in the top-left corner.
Once the provisioning settings in the IdP Directory have been saved, switch back to Parallels My Account and select the **Configuration in the IdP Directory is done** option at the bottom of the section to confirm that you have finished the configuration procedure in the IdP Directory. Then, continue to the next step.
### (6) Add users to the application groups
Add users and administrators to their respective groups created in **Step 3** (described above) to permit them to activate their copies of Parallels Desktop (users) and log into Parallels My Account (administrators) using their corporate login credentials. To do so, switch to the IdP management portal and follow the conventional procedure (as provided by the IdP software) for adding users to the groups. Once it is done, or if you plan to add users later, select the **Configuration in the IdP Directory is done** option at the bottom of the section.
### (7) Configure backup login
The backup login can be used to access your organization’s business account registered with Parallels bypassing Single Sign-On in the event of an SSO malfunction. By default, the backup login is set to the email address of the currently logged-in user. If you want to define a different backup login, add more users first on the Users page of the [Business Profile section](https://my.parallels.com/profile/business/users?role=All\&status=All) in Parallels My Account. The new user must log into the business account at least once before they can be designated as a backup login.
{% hint style="danger" %}
**Warning**: Once you have completed the integration process and activated the SSO functionality, only users from the Administrators group in your IdP signing in via SSO will retain access to managing the Parallels business account. All previous administrative privileges based on logins and passwords will become inactive.
Your designated backup login will continue to work.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://docs.parallels.com/landing/pd-ag/getting-started/configuring-the-single-sign-on-sso-integration-with-parallels-my-account/starting-the-integration-process-in-parallels-my-account/configuring-sso-integration-with-azure-entra-id.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.